

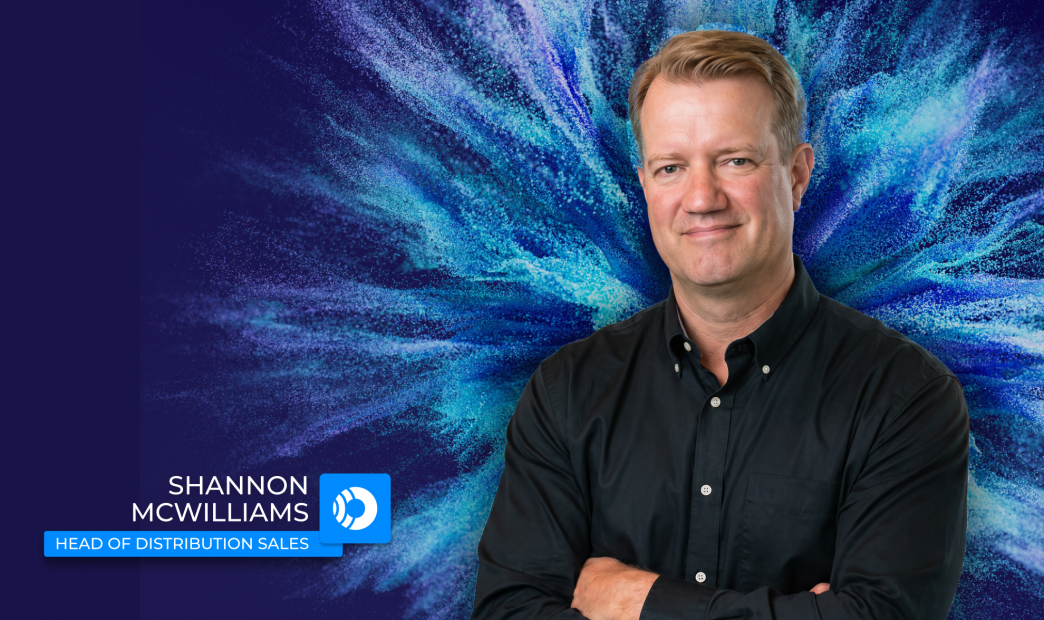
Shannon McWilliams, Head of Distribution, had been at Orca Security a few months when he was asked to look at something specific: what it actually feels like to be one of the company’s reseller partners. How do they experience Orca once they sign on? What are they given to work with?
A partner portal built by someone who isn’t an engineer
The existing answer was a licensed, third-party partner portal. McWilliams tried making small edits to freshen it up, but found the tools underneath it dated. He had used Lovable before, the summer prior to joining Orca, to build and publish a consumer app on his own. So he opened it again and started building a replacement.
McWilliams has spent 20 years in the channel business, working with partners at other companies, and he came into the project with strong opinions about what a good partner experience should include. Using Lovable’s AI features, he built a campaign agent that generates social content for partners, a view into partners’ own Salesforce pipeline so they can track their deals, and a coaching feature meant to help a partner figure out how to move a stalled deal forward. None of it, he says, resembled anything he had seen in two decades of working with partner portals elsewhere.
The weekend it came together
The speed of it was what struck him most. He had run a software development firm in his twenties, with a staff of engineers, and remembers projects like this taking weeks. This one took a weekend.
“I just, over a weekend, started building,” McWilliams says. Within days he had a working version of a new portal, built entirely in Lovable’s natural-language development environment. Orca’s CEO saw the early version and wanted to launch it right away, then asked whether the security team had seen it yet.
What the security review uncovered
“Of course I agree with that,” McWilliams says of the review. “I have some history in software development, so I knew that was going to be a requirement.” He gave Dudi Peretz, the Orca security engineer assigned to the review, full access to the platform and to Lovable itself.
What he hadn’t fully accounted for was how much a non-technical builder can miss without meaning to. Lovable includes its own security scanning tool, and when it told him the app was secure, he took that at face value. It was only through the review process that he understood the difference between a surface-level scan and the kind of check a production application handling partner and customer data actually needs.
A faster kind of fix cycle
The fix cycle that followed became unexpectedly fast. When Peretz’s review turned up an issue, McWilliams would paste the finding directly into Lovable’s AI interface, and the tool would resolve it, often within a few minutes. Peretz would rerun his scans to verify the fix , and the two repeated that loop several times while the product was still being built. An outside firm later ran penetration testing behind the internal review as an additional check before launch.
“It literally took, you know, a day,” McWilliams says, comparing the process to what the same kind of security work would have taken with a traditional engineering team. “That’s what boggled my mind about where we are in software development now.”
A pattern that became part of Orca’s product story
McWilliams doesn’t think the portal was an isolated case, and he doesn’t think Orca is unusual in facing it. “It’s even worse than shadow IT used to be,” he says, “because they’re building apps and pushing things out to the public.” He describes it as a problem nearly every security leader now shares: business builders ship working software with AI, often without engineering or security ever being looped in.
That pattern fed directly into Orca’s own product direction. Within months, the company announced AI AppGen Security, a capability built to discover apps employees build on AI platforms like Lovable, Supabase, and Claude, map what each one touches across APIs, cloud resources, and data, and prioritize which exposures actually matter. Orca’s 2026 State of AI Security Report put a number on the shift: 52% of organizations surveyed said they were already building custom apps with AI.
McWilliams’ portal became one of the earliest internal examples of the exact problem the product was built to address.
What this changes going forward
Since building the partner portal, Orca has replaced a handful of smaller internal software tools with similar business-built apps, saving money across the organization, though nothing on the scale of a core system like Salesforce. McWilliams is candid that this kind of replacement only works because Orca has security staff able to review the work. He suspects many companies without that capability are shipping AI-built tools they believe are secure, because the platform told them so.
He also says the traditional cadence of software releases, building for a quarter and shipping once, doesn’t describe how he works now. He pushes small updates to the portal nearly every day. That pace, he says, is why the review process had to become continuous rather than a single gate before launch.
This is the first of two pieces on the build and review of Orca’s AI-built Partner Portal. The second follows Dudi Peretz, the security engineer who reviewed the software, through what he found and what changed in how Orca approaches business-built software.



 Chat with an Orca Expert