

Executive Summary
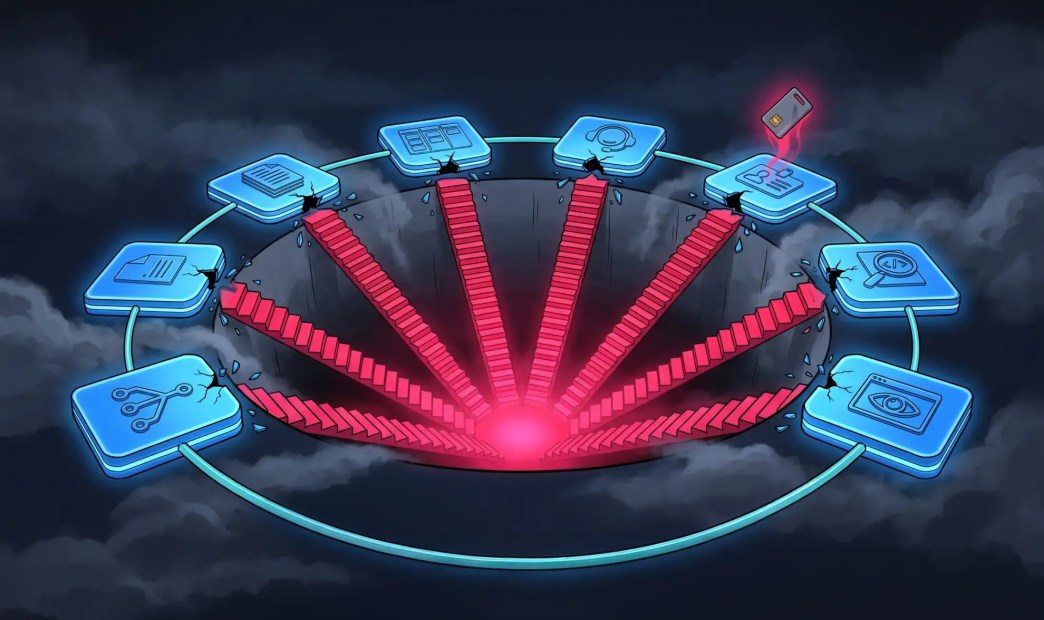
A critical vulnerability (CVE-2026-21589, CVSS 9.3) was disclosed affecting all versions of eight Atlassian Data Center and Server products, allowing attackers to read arbitrary files within the web application root via path traversal. Due to the potential for credential theft and administrative takeover, immediate patching is required.
About CVE-2026-21589
The issue originates from insufficient path validation in the web application layer, where improper input sanitization leads to unauthorized file access. By sending specially crafted HTTP requests with path traversal sequences, unauthenticated remote attackers can read files at known paths within the application root, potentially exposing sensitive configuration data and credentials. No authentication is required to exploit this issue.
Affected systems
The following products are affected: Bitbucket Data Center, Confluence Data Center, Jira Software Data Center, Jira Service Management Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye — all versions prior to the patched releases. These products are widely deployed across enterprise environments for source code management, documentation, project tracking, CI/CD, and identity federation. Organizations using Crowd SSO face elevated risk, as plaintext authentication details stored at predictable file paths can be read and abused to create administrative accounts, potentially granting attackers full control over the entire Atlassian ecosystem.
Users should upgrade to the following fixed versions:
- Bitbucket Data Center: 9.4.26, 10.2.8, or 10.5.1
- Confluence Data Center: 9.2.26 or 10.2.19
- Jira Software Data Center: 9.12.40, 10.3.26, or 11.3.12
- Jira Service Management Data Center: 5.12.40, 10.3.26, or 11.3.12
- Bamboo Data Center: 10.2.24 or 12.1.12
- Crowd Data Center: 6.3.7, 7.0.3, 7.1.7, or 7.2.4
- Crucible: 4.9.15
- Fisheye: 4.9.15
Organizations unable to patch immediately should disconnect affected instances from the internet, apply WAF rules to block path traversal patterns, and review access logs for suspicious activity involving directory traversal sequences.
Risk impact
At the time of writing, no proof-of-concept exploit has been publicly released, and there is no evidence of exploitation in the wild. However, similar Atlassian vulnerabilities have historically been targeted by ransomware operators and APT groups, making rapid weaponization plausible. Regardless, the severity and ease of exploitation make this vulnerability high risk, especially in internet-facing deployments.
Successful exploitation could allow attackers to access sensitive configuration files, harvest plaintext credentials in Crowd SSO environments, and potentially escalate to full administrative control, leading to service disruption, data exposure, or full infrastructure compromise.
How Orca can help
Orca enables customers to quickly identify assets running vulnerable versions of Atlassian products, understand their exposure in context — including internet accessibility, runtime reachability, and asset criticality — and prioritize remediation based on real risk rather than CVSS alone. Orca’s platform highlights affected assets directly in the asset view, helping security teams focus on the most critical remediation paths first.



 Chat with an Orca Expert