

Executive Summary
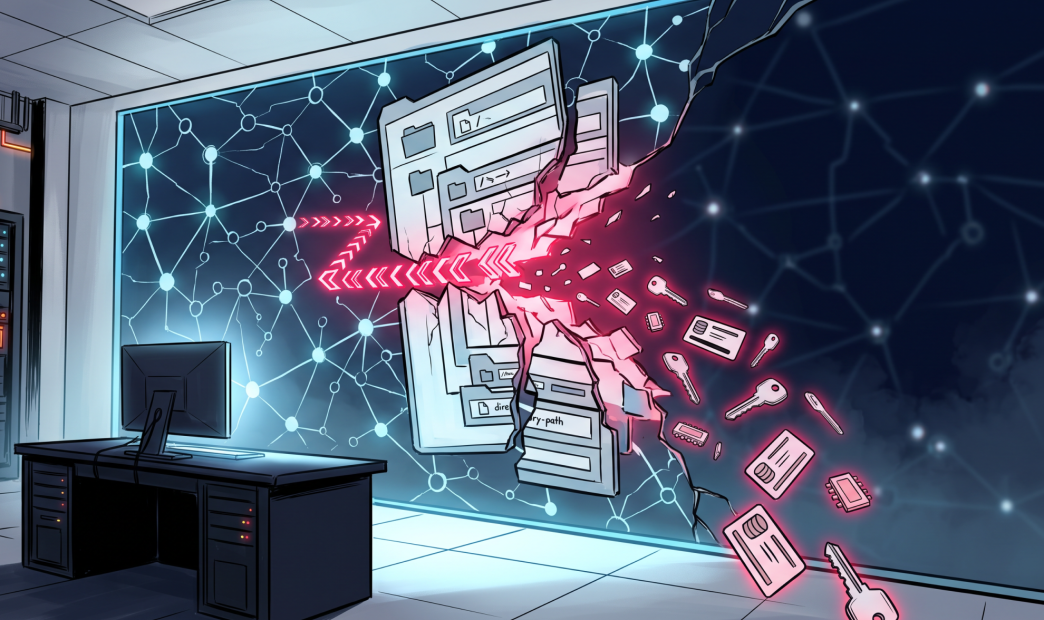
A critical vulnerability (CVE-2026-85706, CVSS 10.0) was disclosed affecting GitLab CE and EE self-managed instances, allowing attackers to read arbitrary server files without authentication via a single HTTP request to the commits API. Due to the potential for complete infrastructure compromise through exposed secrets, immediate patching is required.
About CVE-2026-85706
The issue originates from the repository commits API endpoint (/api/v4/projects/{id}/repository/commits/), where improper path confinement combined with missing authentication enforcement leads to unrestricted file read access on the server. By sending a specially crafted HTTP POST request containing a file.path parameter, attackers can retrieve any file readable by the GitLab process, potentially exposing database credentials, SSH keys, deploy tokens, CI/CD variables, and configuration files. No authentication is required to exploit this issue; the only prerequisite is that at least one public project exists on the target instance.
Affected Systems
The following components are affected: GitLab Community Edition and Enterprise Edition, versions 18.7 through 19.1.7, 19.2.0 through 19.2.5, and 19.3.0 through 19.3.1. These components power source code management, CI/CD pipelines, and DevSecOps workflows across thousands of organizations. Self-managed, internet-facing GitLab instances are at the highest risk.
About CVE-2026-87719
A second critical flaw, CVE-2026-87719 (CVSS 9.9), affects GitLab Enterprise Edition only. An authenticated user with Duo Chat access can exploit an insecure deserialization bug in the GraphQL subscription serializer to bypass serialization controls and retrieve Advanced Search instance configurations, including stored Elasticsearch and OpenSearch passwords. This vulnerability affects GitLab EE versions 18.3 through 19.1.7, 19.2.0 through 19.2.5, and 19.3.0 through 19.3.1.
Remediation
Users should upgrade immediately to GitLab 19.3.2, 19.2.6, or 19.1.8. Multi-node deployments support zero-downtime upgrades. Organizations unable to patch immediately should restrict network access to their GitLab instances by blocking public internet exposure or limiting connectivity to trusted IP ranges. Security teams should review HTTP POST request logs for the commits API endpoint containing file.path parameters to identify potential exploitation attempts. If exploitation is suspected, rotate all secrets stored on or accessible by the GitLab server, including database credentials, SSH keys, deploy tokens, and CI/CD variables.
Risk Impact
At the time of writing, WatchTowr Labs has detected active internet-wide scanning for CVE-2026-85706 beginning September 11 at 06:00 UTC, and CISA has added the vulnerability to its Known Exploited Vulnerabilities catalog with a federal agency remediation deadline of September 14. GitLab.com and GitLab Dedicated customers require no action, as these environments are already protected. Regardless, the maximum severity rating and trivial exploitation requirements make this vulnerability extremely high risk, especially for internet-facing deployments.
Successful exploitation could allow attackers to exfiltrate sensitive configuration files, harvest credentials for lateral movement across connected infrastructure, and potentially achieve full system compromise, leading to service disruption, data exposure, or complete infrastructure takeover.
How can Orca help?
Orca enables customers to quickly identify assets running vulnerable GitLab versions, understand their exposure in context — including internet accessibility, runtime reachability, and asset criticality — and prioritize remediation based on real risk rather than CVSS alone. Orca’s platform highlights affected assets directly in the newItem view, helping security teams focus on the most critical remediation paths first.



 Chat with an Orca Expert