Compliance
Cloud Compliance Solutions for Enterprises: The Automation Checklist
Enterprise teams managing cloud environments across multiple providers and regions know the pain of tracking compliance manually. Spreadsheets fall out...


Enterprise teams managing cloud environments across multiple providers and regions know the pain of tracking compliance manually. Spreadsheets fall out...
Key Takeaways The lifecycle runs in six phases: asset discovery, vulnerability assessment, risk-based prioritization, remediation, verification and rescanning, and reporting...
Key Takeaways An application security framework is a published structure you adopt, apply to your software, and get measured against....
Key Takeaways AI AppGen security covers applications generated by AI app builders and deployed outside traditional development pipelines. The primary...
Key Takeaways A vulnerability scanner is a detection engine, not a program. It finds flaws in a specific class of...
Key Takeaways A cloud security control has four attributes: a function, a class, an owner, and an evidence source. A...
Key Takeaways AI guardrails are runtime controls at three points: the prompt going in, the response coming out, and the...
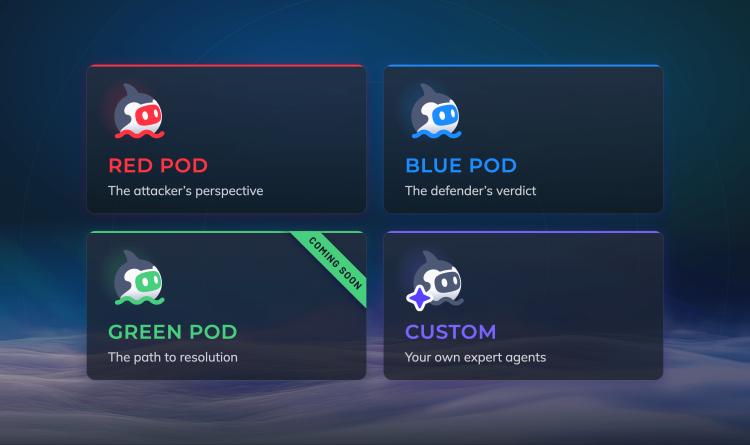
We believe modern security platforms need to enable security for the way your team actually works. In practice, that means...
A compromised GitHub maintainer account was used to publish malicious versions of 10 widely-used npm packages in the keyv and...