

A critical vulnerability in Apache HTTP Server’s mod_http2 module, tracked as CVE-2026-119618 (CVSS 9.8), allows attackers to achieve unauthenticated remote code execution on any server with HTTP/2 enabled. Because exploitation can lead to full server compromise without any authentication, immediate patching is required. The fix is Apache HTTP Server 2.4.71.
CVE-2026-119618 at a glance
| CVE ID | CVE-2026-119618 |
| Severity | CVSS 9.8 (Critical) |
| Weakness | Race condition (CWE-362) leading to heap memory corruption |
| Vulnerable component | assign_headers() function in mod_http2 |
| Authentication required | None |
| Affected versions | Apache HTTP Server 2.4.55 through 2.4.70; standalone mod_h2 2.0.8 through 2.0.42 |
| Fixed version | Apache HTTP Server 2.4.71 |
| Exploitation status | Reliable public exploit demonstrated; no confirmed in-the-wild exploitation at the time of writing |
| Temporary workaround | Disable HTTP/2 by removing h2 and h2c from the Protocols directive |
What is CVE-2026-119618?
CVE-2026-119618 is a race condition in the assign_headers() function of mod_http2, the module that handles HTTP/2 in Apache HTTP Server. The function runs concurrently using shared resources without proper synchronization (CWE-362), and that gap leads to heap memory corruption.
How attackers exploit the mod_http2 race condition
Attackers send specially crafted HTTP/2 requests that trigger the race condition. The resulting heap corruption lets them execute arbitrary code with the privileges of the web server process, potentially leading to full infrastructure compromise. No authentication is required to exploit this issue.
Which Apache HTTP Server versions are affected?
The following components are affected:
- Apache HTTP Server mod_http2, versions 2.4.55 through 2.4.70
- Standalone mod_h2 releases 2.0.8 through 2.0.42
Apache HTTP Server is one of the most widely deployed web servers in the world, and HTTP/2 can be enabled server-wide or per virtual host via the Protocols directive. That means a server can be exposed even if HTTP/2 was only switched on for a single site.
The standalone mod_h2 repository on GitHub has been archived since June 2026, so no standalone fix is available for those releases.
Is CVE-2026-119618 being exploited in the wild?
At the time of writing, public research has demonstrated a reliable exploit against a default mod_http2 configuration, but no confirmed in-the-wild exploitation has been reported. Regardless, the severity and ease of exploitation make this vulnerability high risk, especially in internet-facing deployments.
The vulnerability was independently discovered by Anthropic’s OSS Scanner (reported October 26, 2026) and Google Cloud Vulnerability Research (reported November 3, 2026), underscoring the broad interest in this attack surface.
What can attackers do after exploiting CVE-2026-119618?
Successful exploitation could allow attackers to:
- Execute arbitrary code on the web server
- Pivot to internal networks and backend systems
- Move laterally across the environment, potentially reaching full infrastructure compromise
The business consequences include service disruption and data exposure. Given the wormable potential of this flaw, due to the ubiquity of Apache HTTP Server and its unauthenticated attack surface, organizations should treat remediation as an urgent priority.
How to fix CVE-2026-119618
Upgrade to Apache HTTP Server 2.4.71
Upgrade to Apache HTTP Server 2.4.71 immediately, prioritizing public-facing servers with HTTP/2 enabled. For standalone mod_h2 users, migrating to the bundled mod_http2 in Apache 2.4.71 is the recommended path forward.
Patch status by Linux distribution
| Distribution | Status |
|---|---|
| Red Hat Enterprise Linux 9 | Fixed: mod_http2 update (RHSA-2026:98981) |
| Red Hat Enterprise Linux 10 | Fixed: mod_http2 update (RHSA-2026:98978) |
| Red Hat Enterprise Linux 6, 7, and 8 | Not affected |
| Debian unstable (sid) | Fixed: apache2 2.4.71-1 |
| Debian bookworm, trixie, and forky | Vulnerable, no fix yet |
| Amazon Linux 2, 2023, and 2027 Preview | Fix pending |
| Standalone mod_h2 | No fix (repository archived); migrate to bundled mod_http2 in Apache 2.4.71 |
Temporary workaround: disable HTTP/2
If you can’t patch yet, administrators can disable HTTP/2 by removing h2 and h2c from the Protocols directive, leaving only http/1.1:
Protocols http/1.1
Note this may affect performance for HTTP/2-dependent clients. Check every virtual host as well as the server-wide configuration, since HTTP/2 can be enabled at either level. While patches roll out, keep watching exposed servers for unusual process activity and outbound connections, and use tools that detect and respond to cloud threats to catch post-exploitation behavior such as lateral movement.
How Orca helps you find and prioritize CVE-2026-119618 exposure
Using agentless scanning, Orca enables customers to quickly identify assets running vulnerable versions of Apache HTTP Server. From there, teams can understand their exposure in context (including internet accessibility, runtime reachability, and asset criticality) and prioritize the vulnerabilities that pose real risk rather than relying on CVSS alone.
Orca’s platform highlights affected assets directly in the newItem view, helping security teams focus on the most critical remediation paths first. With attack path analysis, teams can also see whether a vulnerable, internet-facing Apache server sits on a path to sensitive data or critical backend systems, which is exactly the pivot this vulnerability enables.
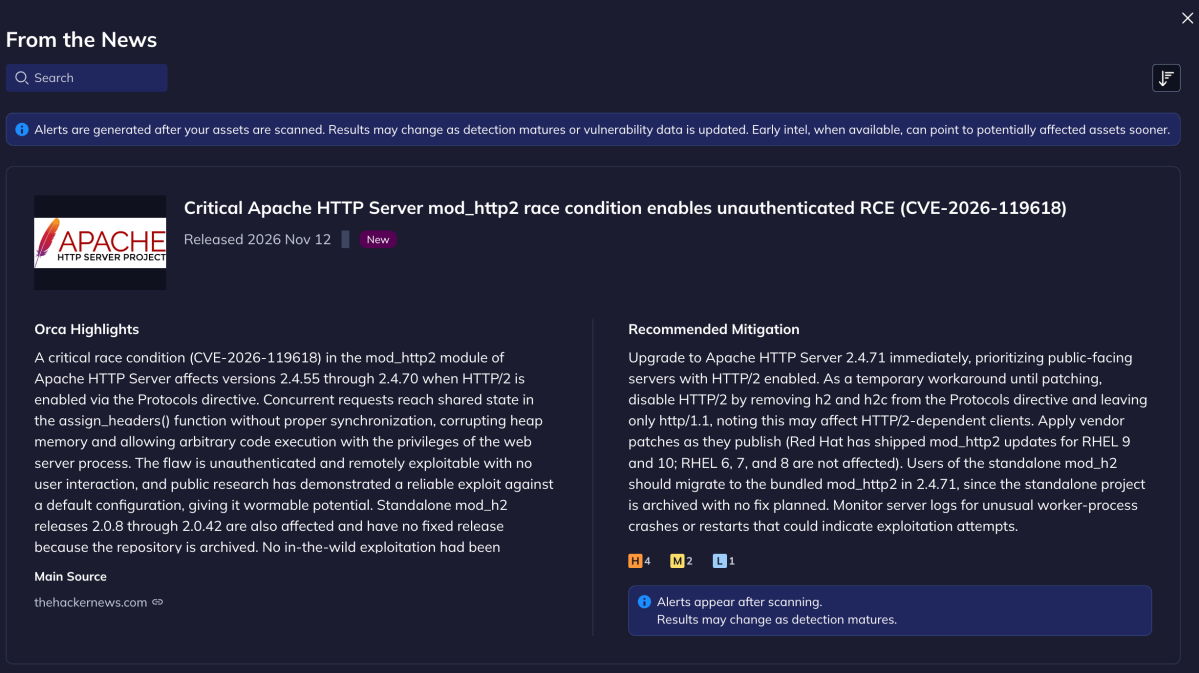
To see how Orca surfaces vulnerable Apache servers alongside the rest of your cloud risk in a unified cloud security platform, schedule a demo.
CVE-2026-119618 FAQ
Does CVE-2026-119618 affect Apache servers without HTTP/2 enabled?
The vulnerability sits in mod_http2, so exploitation requires HTTP/2 to be enabled on the server or on at least one virtual host. That is why removing h2 and h2c from the Protocols directive works as a temporary mitigation.
Which Apache version fixes CVE-2026-119618?
Apache HTTP Server 2.4.71 fixes the vulnerability. Affected versions run from 2.4.55 through 2.4.70.
I run standalone mod_h2. Is there a patch?
No. The standalone mod_h2 repository has been archived since June 2026, so releases 2.0.8 through 2.0.42 won’t receive a standalone fix. Migrate to the mod_http2 module bundled with Apache HTTP Server 2.4.71.
Has CVE-2026-119618 been exploited in the wild?
Not as of this writing. A reliable public exploit has been demonstrated against a default mod_http2 configuration, so treat the risk as high, especially for internet-facing servers.
Which servers should I patch first?
Start with public-facing Apache servers that have HTTP/2 enabled, then servers that can reach sensitive data or backend systems. Exposure context matters more than the CVSS score alone when you’re deciding the order.



 Chat with an Orca Expert