


Introduction
Data used to move at the pace of a migration project. Today it moves at the pace of whoever is building. Developers spin up new databases for a feature branch. Data scientists copy production tables into notebooks to train and evaluate models. Product teams connect foundation models to internal knowledge bases through retrieval-augmented generation (RAG). And with AI app generation tools, people who have never written a line of code are shipping apps that read and write real customer data.
Every one of those builders creates something security teams need to know about. Where is the sensitive data now? Who, and what, can reach it? Which copies did nobody mean to keep? One overly permissive role, one public snapshot, or one vector database full of unmasked customer records is all it takes. Trying to answer those questions with a patchwork of point tools leaves exactly the kind of gaps attackers look for.
That is the job of data security posture management (DSPM). DSPM gives you continuous visibility into your data stores, what they contain, who can access them, and which data is most at risk across your cloud, application, and AI environments. It then helps you act to shrink your data attack surface before it turns into a breach. Not all DSPM solutions are created equal, though. The right one discovers data automatically, connects data risk to the rest of your cloud context, and fits into how your teams already work without adding another tool to manage.
Let’s break down what DSPM is, why it matters more today than it did even a year or two ago, and how to choose an approach that keeps pace with the way companies build in the AI era.
What is DSPM?
Data security posture management (DSPM) is a cybersecurity approach to discovering, classifying, and reducing risk to sensitive data wherever it lives. Gartner introduced the category in 2022 to describe a new class of data security tools built for the cloud rather than retrofitted from on-premises models.
The need has only grown since. Sensitive data now spreads across infrastructure as a service (IaaS), platform as a service (PaaS), and software as a service (SaaS), and increasingly into AI services, training datasets, and vector databases. Much of that data is created and copied by builders outside the security team, so inventories go stale almost as soon as they are written. DSPM closes that visibility gap by continuously mapping data across these diverse, dynamic environments.
[Keep video embed: youtube.com/embed/DnibG0Gumm4]
In this 2-minute video, learn how DSPM identifies misconfigurations, attack paths, anomalies, and other potential data security and compliance risks.
DSPM helps security teams find the conditions that put data at risk, such as public exposure, missing encryption, overly permissive identities, and misconfigured data stores. It then helps them prioritize and fix those issues. Continuous, automated scanning replaces periodic manual audits, so posture reflects what exists and is running today rather than what was documented last quarter.
The benefits are significant. DSPM reduces the risk of data breaches by showing exactly where sensitive data sits and how it could be reached. It supports regulatory compliance by locating, classifying, and monitoring sensitive data covered by privacy laws. And it gives organizations the confidence to adopt AI, because teams can see when regulated data flows into a training pipeline or retrieval index before a model can expose it.
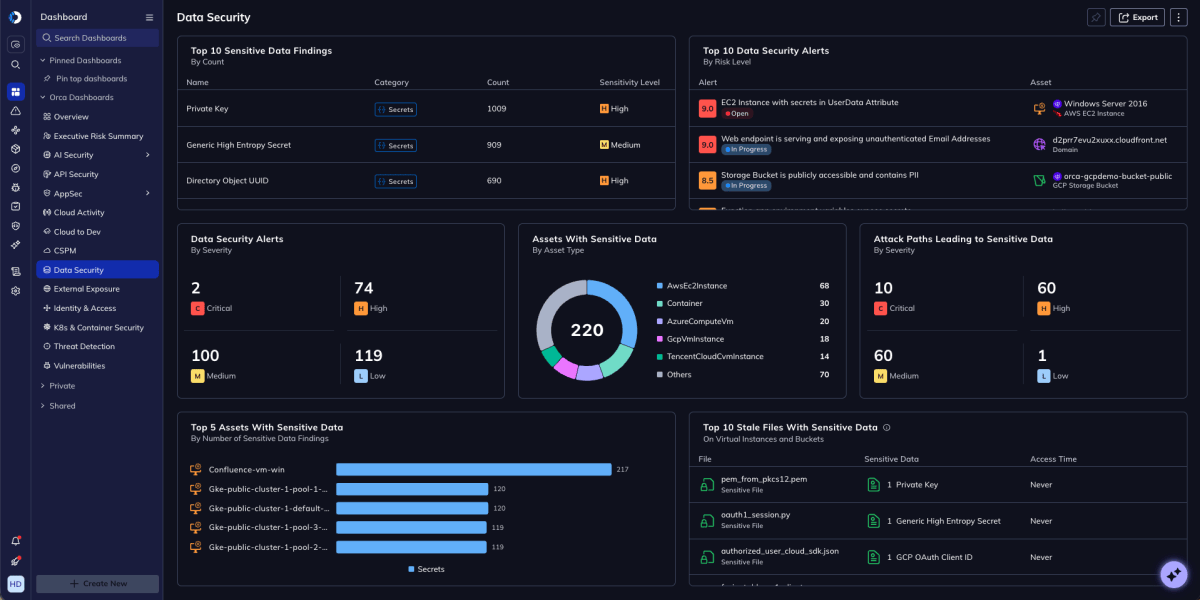
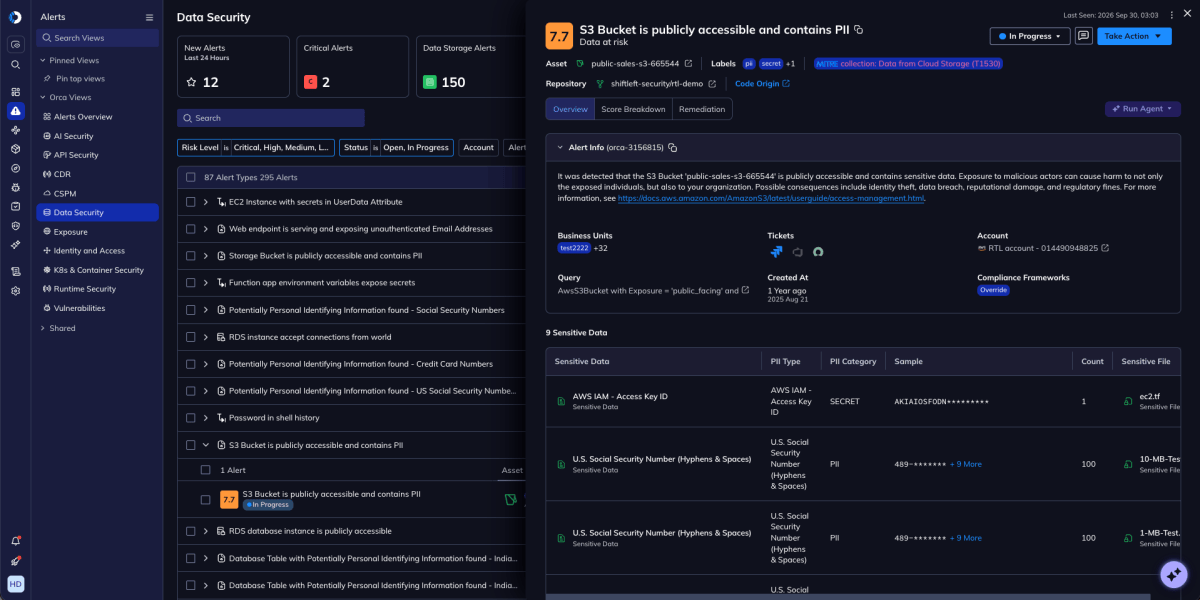
The Orca DSPM dashboard provides key insights into your data security posture
DSPM also differs from adjacent tools. Data loss prevention (DLP) focuses on stopping data from leaving through known channels, and cloud security posture management (CSPM) focuses on cloud configuration risk. DSPM starts from the data itself and asks what is sensitive, where it is, and who or what can reach it. The core capabilities of a DSPM solution include the following.
- Data discovery. Finding sensitive data across managed, unmanaged, and shadow data stores.
- Data classification. Labeling data by type and sensitivity, such as PII, PHI, payment card data, financial records, secrets, and intellectual property.
- Access governance. Mapping every human and non-human identity (NHI) that can reach sensitive data and enforcing least privilege.
- Continuous monitoring. Tracking changes to data stores, permissions, and activity in real-time so new risks surface as they appear.
- Risk assessment. Prioritizing data risks by severity, sensitivity, exposure, and exploitability so teams fix what matters first.
Implementing DSPM takes planning, but the payoff is reducing data breach risk, ensuring compliance, and the freedom to empower teams to innovate without losing track of the data they touch. DSPM is not a silver bullet. It is a critical capability for any organization that builds in the cloud and takes data protection seriously.
Core Components of DSPM
To manage your data security posture effectively, you need visibility into all your sensitive data and how it is accessed. DSPM delivers that through six key components.
1. Data discovery
Continuous data discovery locates sensitive data across every cloud environment, including databases, storage buckets, files on virtual machines, containers, and snapshots. You cannot secure data you do not know exists, and in organizations where anyone can spin up a data store, unknown data is the norm. Effective discovery covers managed services, self-hosted databases, and shadow data, meaning the forgotten backups, test copies, and abandoned buckets that fall outside formal governance. Agentless approaches make this practical at scale because coverage does not depend on developers installing or registering anything.
2. Data classification
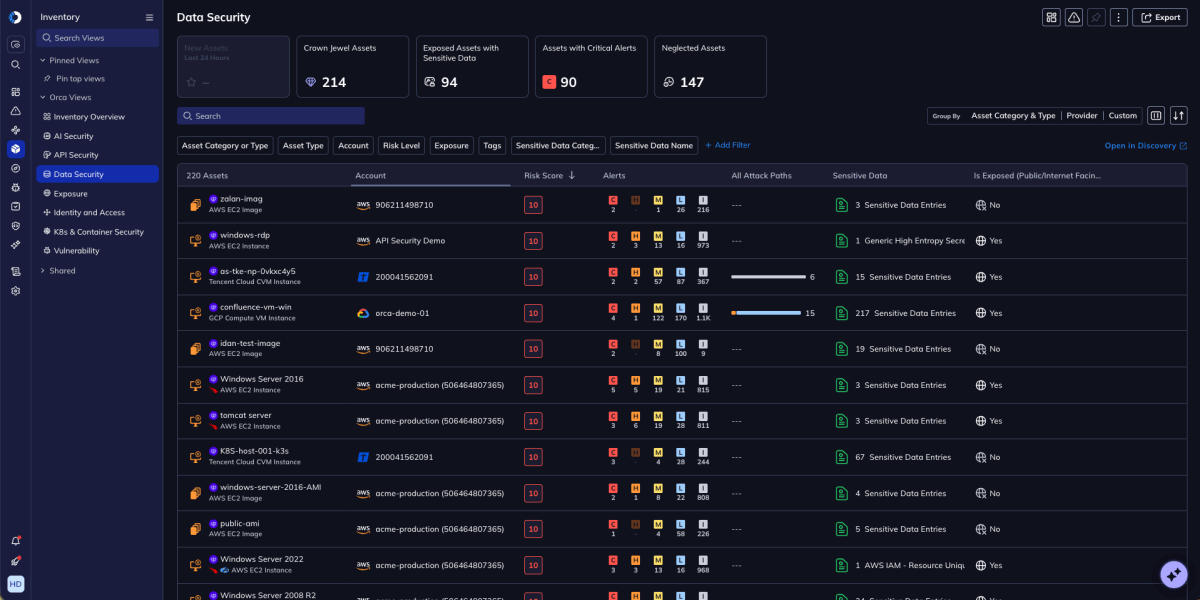
Once data is discovered, DSPM classifies it by sensitivity level, such as public, internal, confidential, or restricted, and by data type, such as PII, PHI, PCI, financial data, and secrets. Some solutions also use optical character recognition (OCR) to find sensitive information inside images such as scanned IDs and passports. Classification helps determine appropriate security controls and access restrictions for your data.
3. Access control
DSPM maps who and what can access sensitive data and whether that access is justified. That least-privilege access control now includes non-human identities such as service accounts, CI/CD pipelines, API keys, and AI agents operating with real cloud permissions. DSPM flags overly permissive roles and unused access, and it watches for suspicious access patterns that could indicate compromised credentials or insider threats.
4. Continuous monitoring and risk assessment
DSPM does not stop at a point-in-time snapshot. It continuously evaluates data environments for vulnerabilities, policy violations, and misconfigurations that could put sensitive data at risk.
5. Coverage for AI data
AI has created new places for sensitive data to hide. Training and fine-tuning datasets, RAG knowledge bases, vector databases, prompt and response logs, and model artifacts can all contain regulated data, often copied from production without the controls that protected the original. DSPM for AI extends discovery and classification into these pipelines. Read more in our guide to DSPM for AI.
6. Remediation
The final step is fixing what monitoring and risk assessment uncover. That could mean revoking unnecessary access, enabling encryption, restricting public exposure, or deleting stale copies of regulated data. Remediation works best when it reaches builders where they already work, through tickets, pull requests, and chat tools, with clear guidance on what to change and why. Automated remediation can resolve some well-understood issues without human intervention.
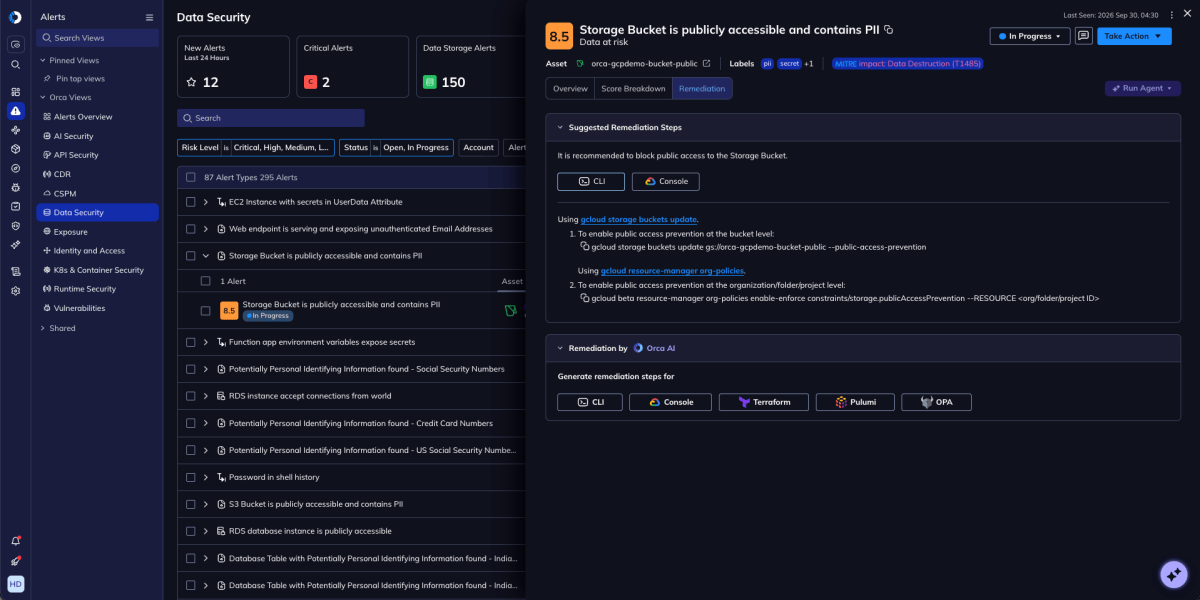
The impact of DSPM on cloud data security
DSPM is essential for protecting sensitive data when cloud, application, and AI environments change daily. By increasing visibility, reducing risk, strengthening compliance, improving governance, and making AI adoption safer, DSPM helps organizations protect their data, finances, and reputation. Here is a breakdown of its impact.
1. Reducing risks from data breaches
Data breaches expose sensitive data, damage customer trust, and cost more every year. According to IBM’s 2026 Cost of a Data Breach Report, the global average cost of a breach reached a record $4.99 million, up 12% from the prior year, and the U.S. average climbed to $11.5 million. The same report found that one in four malicious breaches now involves attackers using AI, and those breaches cost about $1 million more than average. DSPM helps organizations get ahead of that trend by finding data and access risks before attackers do, and by shortening the time it takes to spot unusual activity around sensitive data.
2. Strengthening compliance
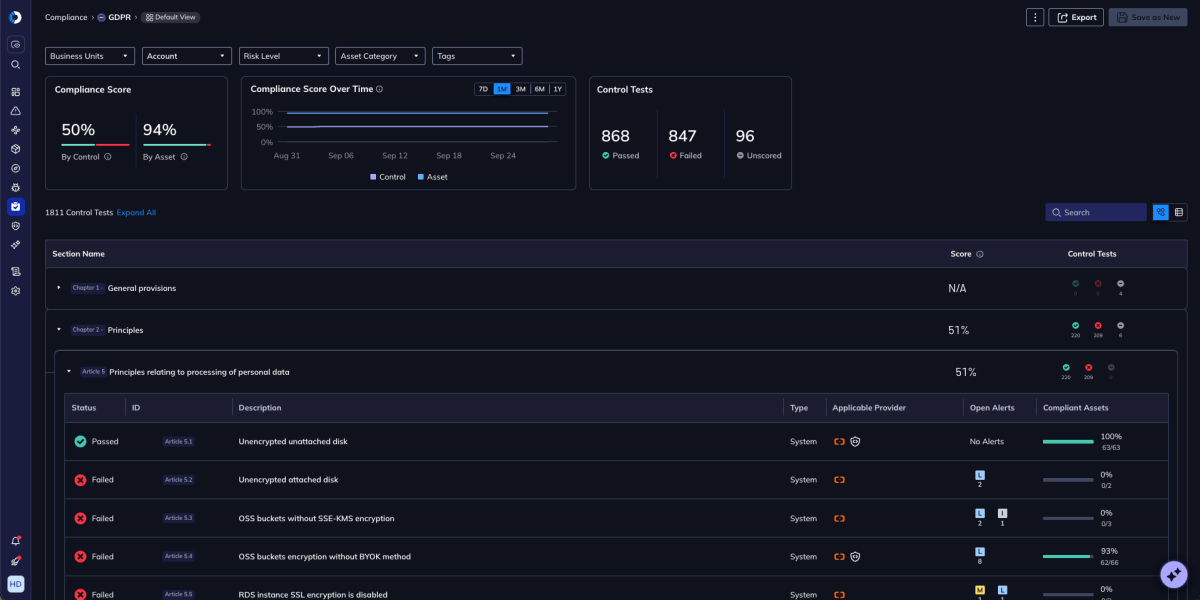
Regulations such as GDPR, HIPAA, PCI DSS, and CCPA require organizations to know where regulated data lives and to control who can access it. AI-specific rules, including the EU AI Act, add expectations for the data used to train and operate AI systems. Compliance is hard to maintain when data stores appear and change daily. DSPM provides the visibility and control to classify data, enforce access policies, and map findings to frameworks continuously, so audits reflect reality rather than an outdated one-time snapshot.
3. Enhancing data governance
Effective data governance depends on knowing what data you have, who owns it, and who can reach it. DSPM catalogs sensitive data across clouds, classifies it by sensitivity, and shows access paths. That helps establish data ownership, set security policies, and hold teams accountable. The foundation matters more as builders across the organization create and share data faster than any manual process can track, and DSPM provides the visibility to govern data properly.
4. Making AI adoption safer
Organizations are connecting AI to their most valuable data at speed. Orca’s 2026 State of AI Security Report found that 64% of AI adopters have deployed vector databases connected to enterprise data. It also found that between 87% and 98% of AI workloads across the major cloud providers lack customer-managed encryption. DSPM gives security teams a way to say yes to AI projects, because they can confirm which data those systems reach and whether it is properly protected.
DSPM implementation and best practices
With the right strategy and tooling, DSPM can secure your data without slowing down the teams who build with it. Here are best practices for implementing DSPM, staying ahead of threats, and protecting data at scale.
Start with discovery
The first step is full visibility into your data landscape, including cloud services, databases, storage, workloads, and AI services. Look for a solution that uses innovative discovery techniques to provide complete cloud coverage and a full data inventory in minutes, without requiring agents or relying on developers to register new resources.
Assess your risks
With a data map in place, evaluate risk by combining data sensitivity with exposure, access, and surrounding cloud risks such as vulnerabilities and lateral movement paths. A good DSPM tool analyzes these factors automatically and ranks findings with context, so your team starts with the issues that would matter most in a real attack.
Remediate high-risk issues
Start with your highest risks, such as publicly exposed databases, overly permissive access controls, or unencrypted sensitive data. Look for a DSPM solution that pairs every finding with clear remediation guidance, supports automated remediation for common issues, and routes work to the owners who can fix it within existing workflows. Orca AI adds guided remediation steps so teams can act quickly.
Continuously monitor
New data stores, permission changes, and AI integrations appear constantly. Effective DSPM monitors continuously for deviations from policy and for anomalous access that could indicate exfiltration. The result is an always-current view of your data security posture rather than a quarterly or annual snapshot.
Define key capabilities
As you evaluate DSPM solutions, look for the following capabilities. For a side-by-side view of the market, see our guide to the best DSPM tools.
- Agentless discovery of sensitive data that runs continuously across your cloud environments
- Coverage for managed and unmanaged databases, object storage, VMs, containers, and serverless functions
- Classification by data type and sensitivity, including PII, PHI, PCI, secrets, and custom types
- Access posture monitoring and anomaly detection for human and non-human identities
- Automated remediation of common misconfigurations, such as public exposure and missing encryption
- Pre-built and customizable compliance reporting that streamlines audits across frameworks
- Integrations with the cloud security, ticketing, and collaboration tools your teams already use
Addressing the security execution gap with DSPM
Cloud environments are dynamic, diverse, and complex—presenting many challenges for data security. The security execution gap refers to the difference between an organization’s data security intentions or policies and their ability to actually execute and implement those policies. DSPM helps bridge this gap by providing continuous visibility and control over sensitive data in the cloud.
With DSPM, you gain insight into where your data resides across clouds, how it’s accessed, and who has privileges. This helps you understand your data risk exposure and prioritize remediation efforts. Say your organization has a policy restricting access to financial data, but without DSPM, you have limited visibility into whether that policy is truly being enforced. DSPM tools automatically discover your data, monitor for policy violations, and alert you to take action.
Continuous monitoring
DSPM continuously watches for changes that affect data security posture. When a new data store is provisioned or an identity’s access changes, DSPM detects it quickly. That vigilance is essential in cloud and AI environments where resources are ephemeral and builders iterate constantly.
Risk-based prioritization
Not all data is equally sensitive, and not every policy violation carries the same risk. DSPM weighs data classification, access, exposure, and surrounding cloud risks to identify the handful of issues that matter most. Teams spend their time where it counts instead of working through a sea of low-impact alerts.
Automated remediation
The execution gap often comes down to limited resources and too many manual processes. DSPM uses automation to streamline data protection at scale, from removing unauthorized access to enabling encryption on unprotected data stores. That frees security teams to focus on higher-level initiatives or more important tasks, and lets builders fix issues quickly without waiting in a queue.
Real-world DSPM use cases
PII data breach prevention
A healthcare organization storing patient records in the cloud uses automated discovery to find unsecured copies of PHI across storage services, including files uploaded by internal tools that no one had inventoried. Applying access controls and encryption to those stores reduces the risk of a HIPAA violation and a costly breach.
Compliance risk remediation
A multinational bank must meet data privacy regulations across regions. DSPM shows where sensitive data lives, who owns it, and who can access it. With that visibility, the bank restricts unauthorized access, deletes unused data, and applies region-specific controls. Continuous monitoring keeps it aligned with GDPR, CCPA, and other regulations as the environment changes.
Reducing cloud data risk
A technology company moving petabytes of data between accounts and clouds uses a CNAPP with built-in DSPM to track risk from misconfigurations, weak access controls, and vulnerabilities throughout the move. Continuous monitoring and guided remediation let the team find and fix issues quickly and migrate with confidence knowing their data was secured according to policy.
Securing data for AI projects
A software company is preparing to launch a customer-facing assistant built on RAG. Before go-live, DSPM reveals that the vector database behind the assistant contains unmasked customer PII and is reachable by an agent with broader permissions than it needs. The team masks the data and tightens access, then ships on schedule.
Consolidating cloud security tools
Rather than manage separate DSPM, CSPM, CWPP, and CIEM tools, a company adopts a CNAPP with integrated DSPM for data security. It replaces point solutions for data discovery, access management, and vulnerability scanning, and it gains end-to-end visibility into data risk from one platform. Eliminating tool sprawl also reduces cost and the time spent reconciling conflicting alerts.
DSPM is only one part of comprehensive cloud security
DSPM is essential, but on its own it cannot see everything that puts data at risk. Attackers rarely go straight for a database. They chain together a vulnerable workload, an exposed API, an overly permissive identity, and a misconfigured data store. That is why data security keeps converging into cloud-native application protection platforms (CNAPP) that cover cloud, application, and AI risk together. A unified approach delivers three key things standalone DSPM cannot.
Complete visibility across cloud and AI environments
A CNAPP brings CSPM, DSPM, CWPP, CIEM, vulnerability management, application security, and AI security into one platform. You see sensitive data alongside the workloads, identities, code, and AI services that touch it, including the shadow AI and AI generated apps that builders create outside formal processes.
Context that powers decisions
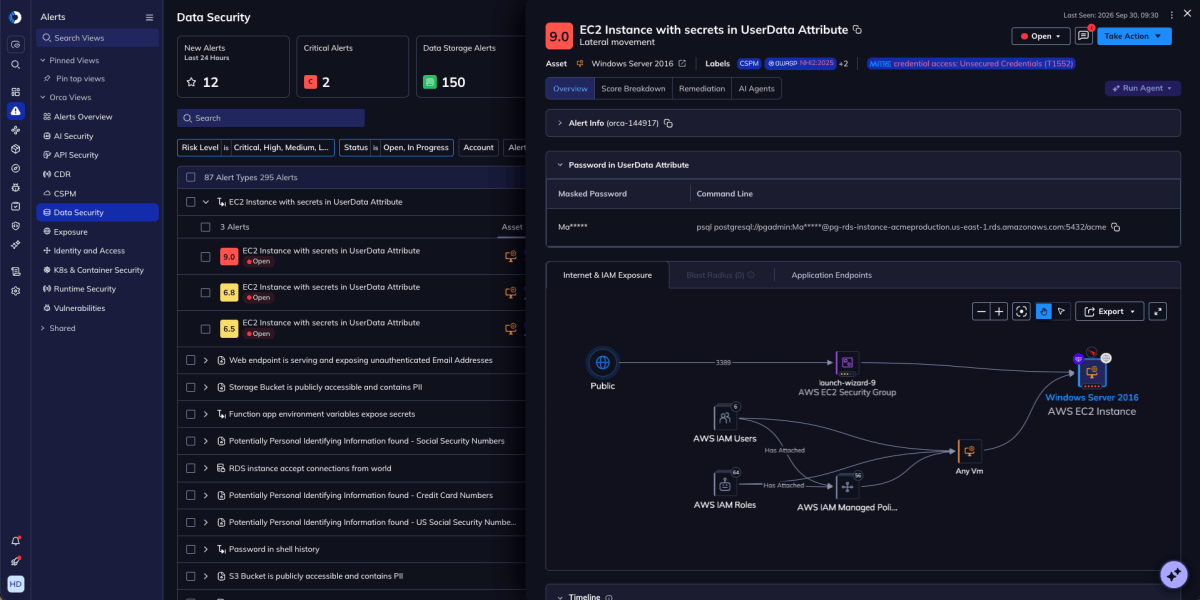
Data risk only makes sense in context. A CNAPP connects data sensitivity to exposure, vulnerabilities, identity risks, and lateral movement paths to show how different risks combine into dangerous attack paths. That context separates the one exposed database that matters from the hundreds of findings that do not.
Security that fits the way you work
Fewer tools mean lower licensing and maintenance costs and less time reconciling conflicting alerts. More importantly, native integrations with ticketing, collaboration, and developer tools such as Jira, Slack, and CI/CD pipelines let teams act on prioritized findings inside the workflows they already use. Security keeps pace with development instead of slowing it down.
Conclusion
Data is no longer created only by a central IT team. Every builder in the organization creates it, across cloud services, applications, and AI pipelines, and it moves faster than manual processes can track. Data security posture management gives security teams continuous visibility into where sensitive data lives, who can access it, and which risks matter most.
Many DSPM tools, however, stop at the data store. Without the surrounding cloud, application, and AI context, they struggle to prioritize and leave teams stitching together findings from separate tools.
Orca Security delivers DSPM as part of the Orca Cloud Security Platform, a CNAPP built on three principles. Complete visibility across cloud and AI environments. Context that powers decisions. Security that fits the way you work. Using agentless SideScanning, Orca discovers and classifies sensitive data across your cloud estate, connects it to every other risk in your environment, and gives teams the guidance they need to fix what matters first.
About Orca Security
Orca Security delivers security for the companies that build. As cloud, applications, AI, and app generation expand the attack surface, Orca transforms security risk into the context teams need to act. The Orca Cloud Security Platform brings data security together with the rest of your cloud, application, and AI security, including the following capabilities.
- Data security posture management (DSPM). Continuously discover, classify, and monitor sensitive data across managed, unmanaged, and shadow data stores, including sensitive data in image files. Get prioritized alerts with masked data samples for fast triage.
- Cloud security posture management (CSPM). Identify misconfigurations and compliance risks across clouds, with prioritized remediation guidance.
- Cloud infrastructure entitlement management (CIEM). Secure cloud identities, users, and entitlements, and enforce least privilege to sensitive data.
- Cloud workload protection (CWPP). Detect vulnerabilities, malware, and risks in virtual machines, containers, Kubernetes, and serverless workloads.
- Application security. Secure cloud-native applications across the SDLC and trace development risks to production.
- AI security. Reduce AI risk across code, posture, and runtime, with a single view of models, AI services, and risk posture.
- AI AppGen Security. Uncover shadow AI app builders and keep them building securely.
- Cloud detection and response (CDR). Monitor around the clock for suspicious activity, including anomalous access to sensitive data.
By unifying these capabilities, Orca helps organizations strengthen data protection, reduce exposure, and maintain continuous compliance across dynamic cloud environments. Schedule a 1:1 demo to see how Orca secures the data your builders create.
Data Security Posture Management FAQs
Data security leaders often have questions about DSPM and how to implement it. Here are answers to some of the most common ones.
What differentiates CNAPP from DSPM?
CNAPP stands for cloud-native application protection platform. DSPM focuses specifically on securing sensitive data, while a CNAPP takes a broader approach. In addition to DSPM capabilities like data discovery and classification, a CNAPP provides posture management, workload protection, identity and entitlement management, container security, API security, application security, AI security, and more. Some CNAPPs, like Orca Security, fully integrate DSPM so data risk is prioritized alongside every other cloud risk.
What is the difference between DLP and DSPM?
Data loss prevention (DLP) tools are designed to detect and block sensitive data from leaving the organization through known channels. DSPM has a wider scope. It continuously discovers and classifies data at rest, assesses who can access it, and identifies the posture risks that could lead to exposure in the first place. The two are complementary, and DSPM findings can inform where DLP controls matter most.
What is DSPM for AI?
DSPM for AI extends data discovery and classification into AI pipelines, including training and fine-tuning datasets, RAG knowledge bases, vector databases, and prompt and response logs. It helps teams catch regulated data before it enters a model or retrieval index, and it shows which models and agents can reach sensitive data. Learn more in our guide to DSPM for AI.
How is DSPM different from AI-SPM?
AI security posture management (AI-SPM) focuses on the security of AI systems themselves, such as model endpoints, AI services, packages, credentials, and agent configurations. DSPM focuses on the data those systems use and produce. Together they answer two related questions. Is the AI system configured securely, and is the data it touches protected?
How does DSPM enhance multi-cloud security?
DSPM gives organizations visibility into sensitive data distributed across multiple public clouds, private data centers, SaaS apps, and AI services. By discovering, monitoring, and remediating risks in diverse environments, DSPM closes security gaps that would otherwise stay invisible. It also simplifies compliance by providing a single view of data governance controls across every cloud.
What are the steps in deploying a DSPM strategy?
Follow these steps to implement DSPM.
- Discover and catalog where sensitive data resides across your cloud, application, and AI environments.
- Classify data by sensitivity, importance, and regulatory scope.
- Evaluate access for human and non-human identities and enforce least privilege.
- Continuously monitor for data security risks, changes, and anomalous access.
- Remediate identified issues, starting with those on active attack paths.
- Define data security metrics and KPIs to measure your posture over time.
How do you measure data security posture?
Key metrics for evaluating data security posture include the following.
- Percentage of data stores discovered and classified, including shadow data
- Number of data stores with public exposure, excessive access, or weak authentication
- Mean time to discover and remediate critical data risks
- Share of AI data stores with sensitive data that are properly protected
- Compliance with data protection regulations and internal policies
- Trends in data risk over time
Continuously tracking and improving these metrics strengthens your overall data security posture. DSPM solutions provide reports and dashboards to follow these KPIs across your organization.



 Chat with an Orca Expert